Cloud Security
DevSecOps vs DevOps: How to Integrate Security Without Slowing Delivery
DevSecOps adds automated security checks to the development pipeline, preventing costly fixes after code reaches production environments.
DevSecOps adds automated security checks to the development pipeline, preventing costly fixes after code reaches production environments.
Replacing servers instead of patching them eliminates configuration drift and reduces the attack surface for persistent threats.
Technical controls fail when staff ignore them; culture turns employees into active defenders who spot threats before breaches occur.
Session tokens often bypass multi-factor authentication, allowing attackers to enter networks without triggering standard login alerts or password checks.
Multi-factor authentication blocks credential theft even when passwords are compromised, offering high security with minimal operational overhead for small teams.
Network traffic analysis reveals hidden lateral movement by mapping packet flows, exposing threats that endpoint sensors miss entirely.
Understanding attack phases reveals that most small businesses fail at detection, not prevention, leaving critical windows for silent data exfiltration.
Treating security as a static checklist creates blind spots where attackers exploit the gap between policy and actual system behavior.
Most cracking attacks succeed not by breaking encryption but by exploiting weak implementation and predictable user behavior patterns.
Excessive notifications desensitize analysts to genuine threats, causing them to miss subtle indicators of compromise that require careful investigation.
Endpoint telemetry transforms raw device logs into actionable intelligence, allowing you to detect sophisticated threats that traditional antivirus software misses entirely.
Command injection occurs when untrusted input executes system commands, bypassing application logic to access files or control servers directly.
Attackers use lateral movement to bypass perimeter defenses by hopping between internal systems, making early detection the only effective countermeasure.
Most security fixes introduce new vulnerabilities because teams verify the patch but ignore the surrounding code paths that changed during the repair.
Output encoding stops most cross-site scripting attacks, while input validation alone leaves your application exposed to sophisticated injection techniques.
Cloud incident response differs from on-premise recovery because you lack physical control over the underlying infrastructure, requiring a shift toward identity-based containment.
Honeytokens are silent tripwires that detect data exfiltration and credential theft without requiring network monitoring or active defense systems.
Large language models introduce prompt injection risks that traditional web security controls cannot detect or block effectively.
Disabling deserialization entirely eliminates the threat, while input validation alone fails because attackers bypass filters using encoded payloads that look harmless to basic checks.
True resilience requires testing failure paths in production-like environments, not just relying on geographic redundancy that masks logical single points of failure.
Firmware flaws bypass operating system security controls and allow attackers to maintain persistent access even after a complete system reinstallation or hardware replacement.
Physical observation bypasses encryption, making your entry of credentials the single weakest link in any digital security posture regardless of software strength.
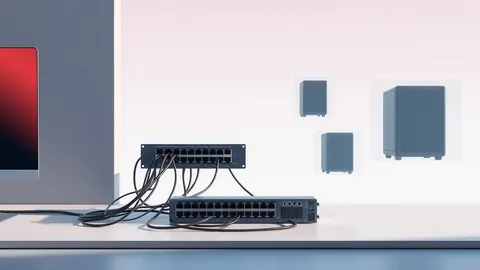
VLANs isolate traffic at the network layer using hardware switches, while microsegmentation applies identity-based rules to individual workloads regardless of their network location.
Incident response is not just a technical fix but a legal and operational framework that dictates how your organization survives and recovers from a security breach.