Cloud Security
Fix Service Account Security: 6 Common Misunderstandings
Service accounts often hold more power than human employees because they lack behavioral baselines that trigger automated anomaly detection systems.
Cloud Security coverage from Shell Bulletin holds 19 articles, 17 of them reference guides. The newest was published on October 14, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include NIST Cybersecurity Framework and Cloud Security Alliance.
Service accounts often hold more power than human employees because they lack behavioral baselines that trigger automated anomaly detection systems.
Most account takeovers succeed because attackers exploit weak identity policies and stale permissions rather than breaking encryption algorithms.
DevSecOps adds automated security checks to the development pipeline, preventing costly fixes after code reaches production environments.
Replacing servers instead of patching them eliminates configuration drift and reduces the attack surface for persistent threats.
Cloud incident response differs from on-premise recovery because you lack physical control over the underlying infrastructure, requiring a shift toward identity-based containment.
True resilience requires testing failure paths in production-like environments, not just relying on geographic redundancy that masks logical single points of failure.
A new industry report argues that strengthening identity access management is the foundational requirement for effective cyber resilience in cloud-heavy environments.
VLANs isolate traffic at the network layer using hardware switches, while microsegmentation applies identity-based rules to individual workloads regardless of their network location.
Specialized AI clouds hit $9 billion in Q4 2025, but unclear provider messaging keeps many enterprises from adopting the technology.
Most cloud breaches occur because administrators grant permanent, broad permissions that remain active long after the original project ends.
Multi-cloud security fails when it treats providers as separate entities rather than a unified identity fabric that enforces policy across all environments simultaneously.
Private endpoints route traffic through a deterministic private network path, bypassing the public internet to eliminate exposure from unsecured cloud databases.
Data residency dictates that the physical server holding your information must remain within specific legal borders, creating a hidden operational burden that most teams ignore.
Zero trust network access shifts security from the network edge to the individual workload, ensuring that no connection is trusted by default regardless of its origin or destination.
Most container breaches occur after deployment, meaning image scanning alone fails to stop attackers who compromise the running environment through misconfigurations.
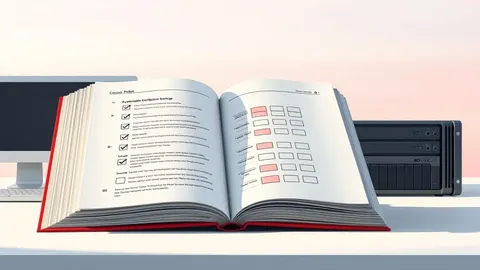
These free configuration standards turn vague security goals into specific, auditable settings for your operating systems and cloud services.
Most database leaks stem from forgotten public access flags, not sophisticated hacking, making access controls your highest priority.
Workload identity replaces static credentials with short-lived tokens, preventing attackers from hijacking services even if they breach your network perimeter.
Most data leaks occur not because hackers break through walls, but because owners leave the back door unlocked by keeping factory default settings.