Data Breaches
Dark Web Monitoring: 8 Real Questions Answered for Security
Dark web monitoring reveals stolen credentials and exposed data before attackers can exploit them, but it cannot stop the initial theft that made the data available.
Data Breaches coverage from Shell Bulletin holds 16 articles, 16 of them reference guides. The newest was published on October 14, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include UK Information Commissioner's Office and IdentityTheft.gov (FTC).
Dark web monitoring reveals stolen credentials and exposed data before attackers can exploit them, but it cannot stop the initial theft that made the data available.
Data loss prevention systems monitor data in motion and at rest to block unauthorized transfers before they leave your network perimeter.
Full disk encryption protects data at rest but leaves information exposed while the system runs or during transmission.
Paid monitoring services detect data exposure after the fact and offer recovery assistance, but they cannot prevent the initial compromise of your personal information.
Compliance requires mapping data flows before configuring controls, a step often skipped until audits fail during the discovery phase.
Email encryption splits your message into separate pieces, sending the data through public channels while keeping the decryption key in a private vault that only the recipient controls.
The HIPAA Security Rule defines required safeguards through addressable specifications, allowing organizations to implement equivalent controls if standard measures are technically infeasible.
Treating confidentiality, integrity, and availability as equal priorities often creates blind spots that attackers exploit during an incident.
Your passwords are likely already compromised in public databases, making unique passphrases and multi-factor authentication the only reliable defense against automated account takeover.
Keeping data longer than necessary increases your attack surface and legal liability, while deleting it too soon violates compliance requirements.
Notification timing often depends on your internal investigation speed, not just the clock, creating a hidden compliance risk for small teams.
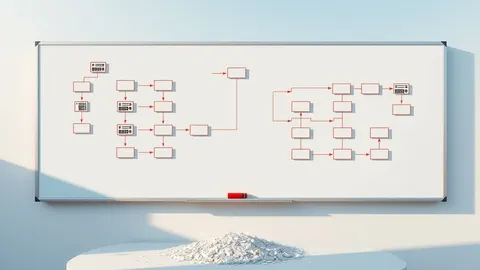
Compliance is a structural audit of controls, not a guarantee of security, and scoping determines your actual workload more than your revenue does.
Storing data longer than necessary increases your attack surface and legal liability without providing operational value or business continuity benefits.
Delaying breach notification often violates legal mandates before the technical impact is fully understood, creating liability that outlasts the intrusion.
Keeping logs forever creates a liability trap because old records often contain outdated security controls and stale personal data that attract attackers.
Recycled login details from old breaches allow attackers to bypass modern security layers without needing new hacking tools or complex exploits.