Malware & Ransomware
Malware Analysis for Small Business: Practical Steps and Limits
You can identify basic threats using file hashes and static inspection, but sophisticated attacks require dynamic analysis in isolated environments.
You can identify basic threats using file hashes and static inspection, but sophisticated attacks require dynamic analysis in isolated environments.
Potentially unwanted programs hide in plain sight, using legitimate software behaviors to install tracking tools that degrade system performance and privacy.
Computer viruses require human action to spread, unlike worms that move automatically, making user behavior the primary control point.
Voice phishing exploits the psychological weight of spoken urgency, bypassing the visual scrutiny you apply to written messages.
Delaying breach notification often violates legal mandates before the technical impact is fully understood, creating liability that outlasts the intrusion.
Buffer overflows often manifest as intermittent application crashes before they become exploitable, allowing you to identify memory corruption bugs before an attacker does.
Automating low-value tasks reduces alert fatigue, but poor logic design creates faster failure modes that bypass human oversight entirely.
Keeping logs forever creates a liability trap because old records often contain outdated security controls and stale personal data that attract attackers.
File hashes provide a deterministic method to identify known threats, yet they fail against code that changes its appearance without altering its function.
Recycled login details from old breaches allow attackers to bypass modern security layers without needing new hacking tools or complex exploits.
Malware payloads rarely execute immediately upon download, instead relying on delayed triggers and system hooks to maintain persistence and evade initial detection mechanisms.
Banking trojans often survive system wipes by rewriting firmware or stealing credentials before you notice the infection, making credential rotation mandatory.
Disabling macros entirely is the only setting that stops all Office-based attacks, but it breaks legacy workflows that rely on automation scripts.
Standardized response procedures reduce human error during crises but often fail when facing novel threats or complex, multi-stage intrusions that defy simple categorization.
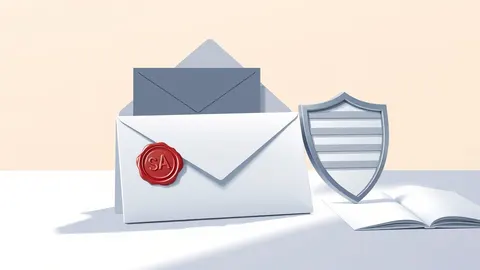
DKIM proves the message content is intact, while DMARC dictates policy for messages that fail authentication checks, preventing domain spoofing.
Hidden command and control channels often bypass standard firewalls by masquerading as legitimate DNS or HTTPS traffic, making detection difficult without specific monitoring.
Map threats to your data, build specific alerts, and validate them to stop attacks before they cause damage.
Move beyond vanity counts to metrics that reveal true risk exposure and operational efficiency for your organization.